Security Architecture
A comprehensive technical overview of Akshar Group Technologies’ multi-layered defense-in-depth posture, DevSecOps pipelines, cloud infrastructure hardening, data encryption, and incident response protocols.
Secure by Design, Resilient by Architecture
At Akshar Group Technologies, security is not an afterthought or an add-on module. Every ERP implementation, commerce platform, and custom software architecture is designed from day one to withstand sophisticated adversarial threats.
Zero Trust Philosophy & Defense-in-Depth
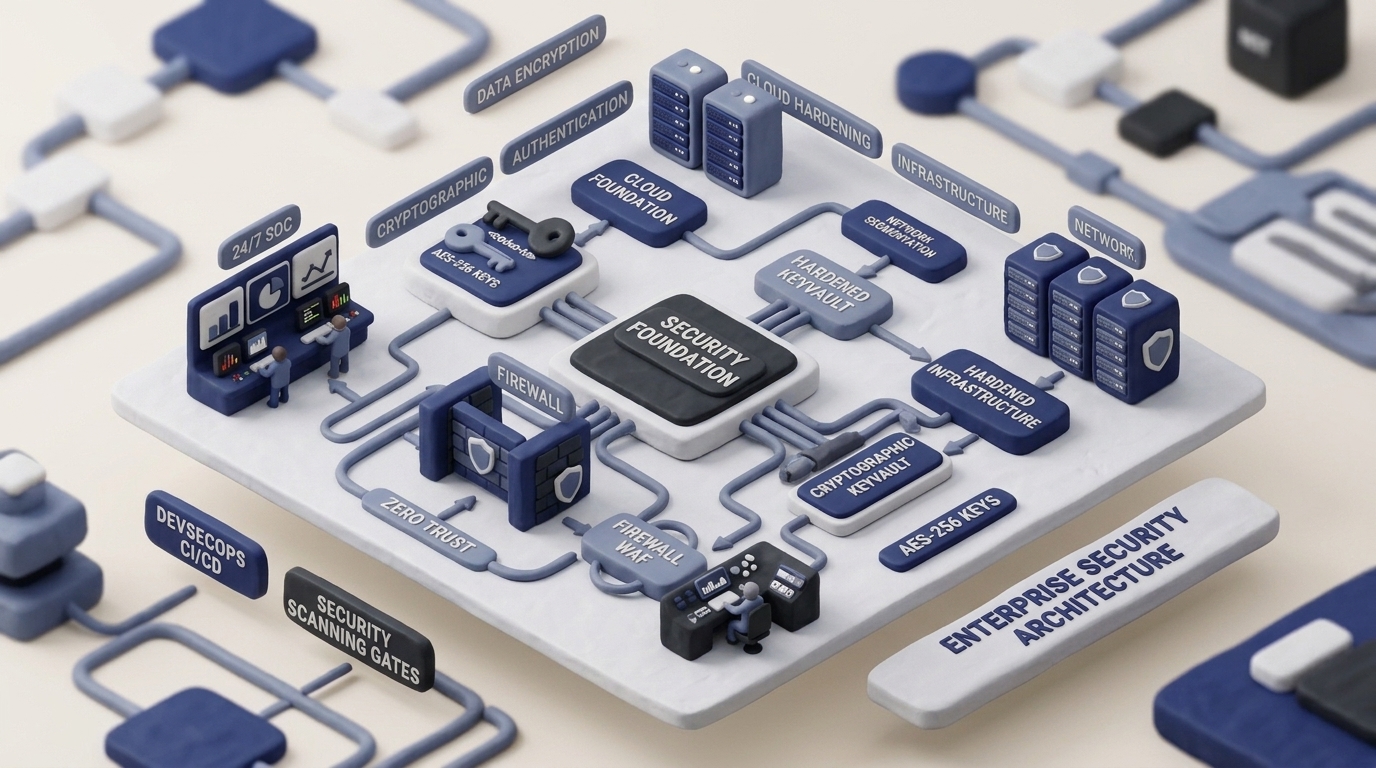
We operate under a strict "Never Trust, Always Verify" architectural paradigm. Every request, endpoint, microservice, and user identity is authenticated, authorized, and cryptographically verified at every layer.
- Principle of Least Privilege (PoLP) enforced across all staging, build, and production workloads.
- Micro-segmentation isolating network environments, database clusters, and background worker queues.
- Ephemeral session tokens with automated expiration, rotation, and multi-factor re-authentication.
Cloud Infrastructure & Perimeter Hardening
Enterprise cloud deployments hosted on hardened AWS, Google Cloud, and Azure environments with multi-layered perimeter firewalls and DDoS mitigation.
- Enterprise WAF (Web Application Firewall) blocking SQL injections, cross-site scripting (XSS), and malicious bots.
- Private VPC subnets with zero direct public IP exposure for relational databases and Redis caching tiers.
- Automated DDoS attack absorption and edge rate-limiting via globally distributed CDN edge networks (Cloudflare/CloudFront).
Application Security & DevSecOps CI/CD Pipeline
Security is integrated into every phase of our software development lifecycle (SDLC), from initial architectural review to automated deployment gates.
- Automated SAST (Static Application Security Testing) and DAST (Dynamic Testing) scanning on every Git pull request.
- Automated Software Composition Analysis (SCA) blocking known CVE vulnerabilities in npm, pip, and composer dependencies.
- Pre-commit git hooks and secret scanners preventing accidental commits of API keys, tokens, or private credentials.
Data Protection & Cryptographic Protocols
We employ bank-grade encryption across all states of data lifecycle to ensure total confidentiality and integrity.
- Data at Rest: Encrypted using AES-256 with envelope encryption and automated annual/on-demand KMS key rotation.
- Data in Transit: Enforced TLS 1.3 encryption across all client-to-server and inter-service API communications.
- Field-level database encryption for sensitive PII, authentication salts, and client configuration secrets.
Identity & Access Management (IAM)
Granular identity governance ensuring that only authorized personnel can access infrastructure under strict audit logging.
- Mandatory Multi-Factor Authentication (MFA) via FIDO2 WebAuthn / hardware keys for all developer and admin accounts.
- Enterprise SSO / SAML 2.0 integration for seamless enterprise workforce identity federation.
- Role-Based Access Control (RBAC) with time-bound, just-in-time (JIT) elevated access permissions.
Enterprise ERP & Commerce Hardening
Specialized security frameworks tailored for high-volume Odoo ERP, Magento/Adobe Commerce, and Shopify Plus ecosystems.
- Odoo ERP: Custom module security audits, restricted XML-RPC access, PostgreSQL row-level security policies.
- Digital Commerce: Strict PCI-DSS compliance alignment, tokenized payment gateway handoffs with zero on-server credit card storage.
- Rate-limited checkout APIs preventing brute-force coupon enumeration and card-testing bot attacks.
Vulnerability Management & Penetration Testing
Continuous security discovery through automated scanning, scheduled third-party penetration testing, and ethical disclosure programs.
- Bi-annual independent third-party black-box and white-box penetration testing.
- Continuous automated vulnerability scanning across container registries and host OS dependencies.
- Structured Responsible Disclosure and Bug Bounty intake channel for ethical security researchers.
Disaster Recovery & Business Continuity (BCDR)
High-resilience architecture engineered to prevent data loss and ensure rapid failover in catastrophic scenarios.
- Geo-redundant automated snapshots and point-in-time database recovery (PITR).
- Target Recovery Point Objective (RPO) of < 1 hour and Recovery Time Objective (RTO) of < 4 hours.
- Quarterly simulated disaster recovery and database restoration drills to verify failover integrity.
Compliance, Governance & Regulatory Alignment
Our architectural standards and operating procedures align with premier global regulatory frameworks.
- GDPR & UK GDPR full data controller/processor compliance readiness.
- Operational alignment with ISO/IEC 27001 information security management standards and SOC 2 Type II trust criteria.
- OWASP Application Security Verification Standard (ASVS) Level 2 adherence for custom web and mobile apps.
24/7 Threat Monitoring & Incident Response Runbook
Continuous telemetry, centralized SIEM event auditing, and immediate incident mitigation protocols.
- Centralized audit logging with immutable, write-once-read-many (WORM) storage for forensic analysis.
- Real-time anomaly detection and automated alert escalation via PagerDuty to on-call security architects.
- Strict 15-minute response SLA for critical severity security incidents and 72-hour regulatory breach notification procedures.
Report a Security Vulnerability
Akshar Group Technologies values the contributions of the global security research community. If you believe you have discovered a vulnerability or security flaw in any AGT service, system, or client repository, please submit your findings to our dedicated security response team.
- Provide a detailed Proof-of-Concept (PoC) with step-by-step reproduction instructions.
- Do not access, modify, or delete customer or proprietary data without explicit authorization.
- Allow reasonable time for our engineering squad to patch the vulnerability before public disclosure.
- We commit to acknowledging your report within 24 business hours and providing regular remediation status updates.